Todaytrace AI
An AI assistant for SOC teams that triages and investigates SIEM alerts, summarizes what happened, maps it to MITRE ATT&CK and suggests a response, with the analyst making the call.
A system we build for organizations
An AI assistant for SOC teams that triages and investigates SIEM alerts, summarizes what happened, maps it to MITRE ATT&CK and suggests a response, with the analyst making the call.
A system we build for organizations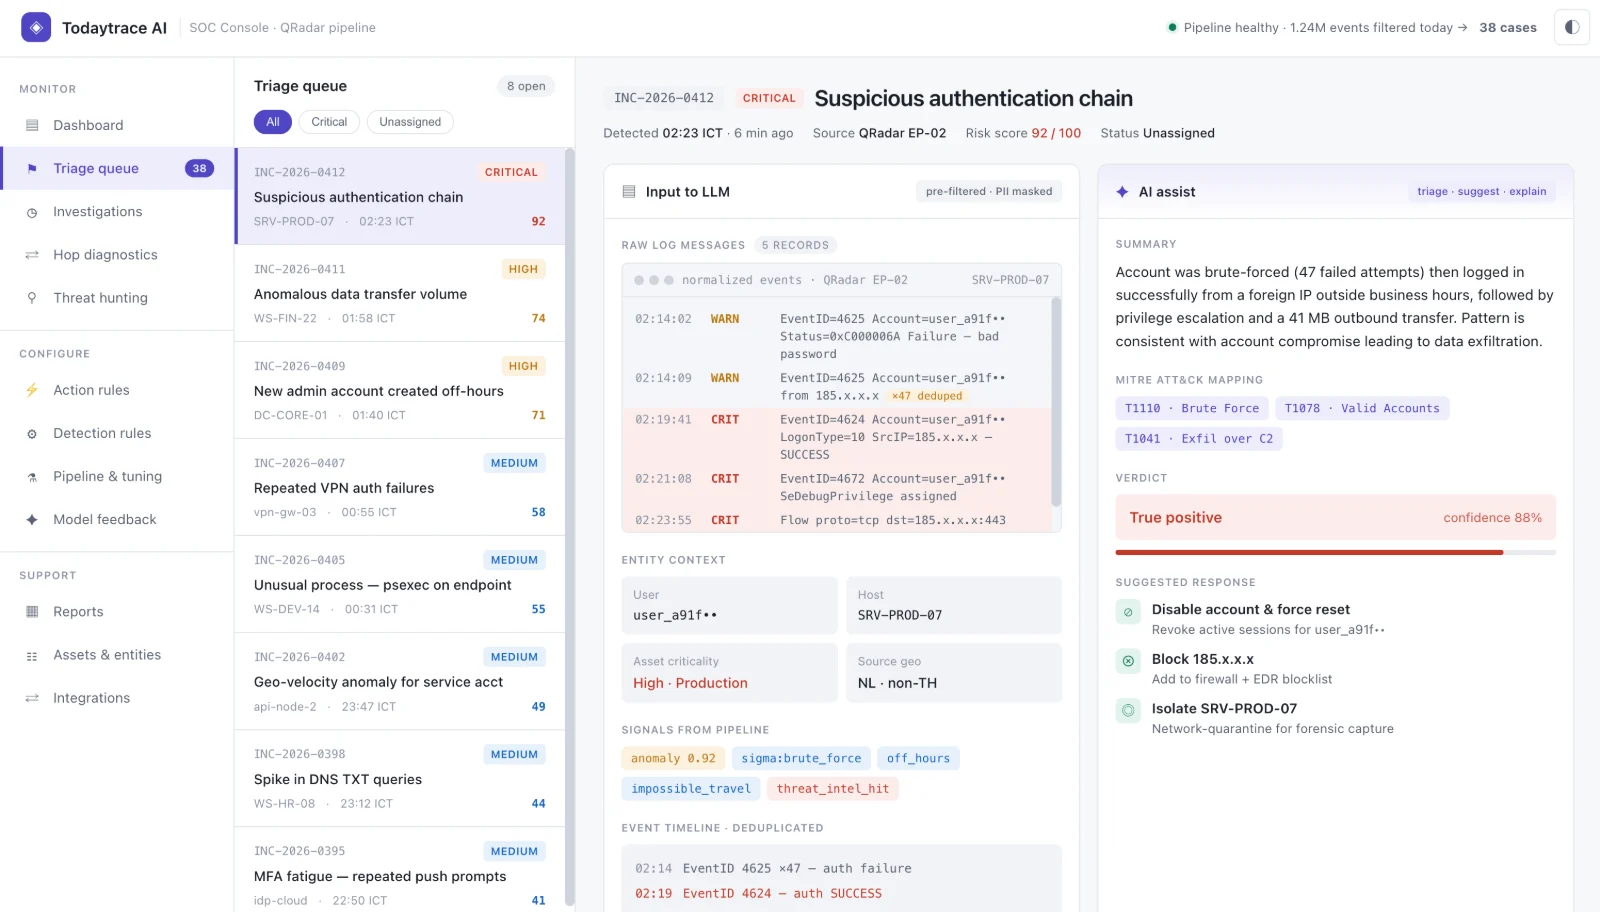
The SIEM raises more alerts than the team can read. Analysts go through raw logs line by line, gather context from several tools, and the alerts that matter get lost in the noise.
Alerts are filtered and deduplicated before they reach people. Each case arrives with a summary, a risk score, user and host context, and a suggested response you can check.
You want less time on triage and more on the cases that matter.
It connects to the SIEM you already run, whichever vendor it is.
Start with Wazuh, an open-source SIEM we provide and run.
Cases ranked by a 0–100 risk score, filtered by severity and owner
What happened, in plain words, with a verdict and its confidence
Behavior in each case mapped to ATT&CK techniques
User, host, asset criticality, source location and a deduplicated timeline
Such as disabling an account, blocking an IP or isolating a host; what runs automatically is set in action rules
Detection rules, pipeline tuning, model feedback and threat hunting
Targets are agreed during Discovery, and real results are reported after the pilot.
| Who operates it | Where data lives | Best for | |
|---|---|---|---|
| Managed cloud | We operate everything | A region you choose | Fastest start, no infrastructure team needed |
| Your cloud | We deploy into your cloud account | Stays in your account | Organizations with an existing cloud policy |
| On-premise | Installed in your data center | Never leaves your premises | Data with the strictest requirements |
Answer 13 questions in about 5 minutes. You get a readiness score across 6 areas and a first scope to start from.